Chinese Hackers Exploit Vulnerabilities in Microsoft SharePoint Servers
Microsoft has reported that hackers linked to China, including state-sponsored groups, have taken advantage of security flaws in its SharePoint document-sharing software to target data belonging to businesses that use it.
The company identified three groups—Linen Typhoon and Violet Typhoon, which have ties to the Chinese government, and Storm-2603, believed to operate from China—using recently uncovered vulnerabilities to attack internet-connected servers running the platform.
This disclosure follows reports of Amazon closing its artificial intelligence lab in Shanghai, while consultancy McKinsey has halted AI-related work in China as tensions between Washington and Beijing intensify.
Microsoft and IBM have also reduced research and development projects in China, coinciding with heightened U.S. scrutiny of American firms involved in AI development there.
According to Microsoft, the vulnerabilities affect on-premises SharePoint servers used by many companies but do not impact its cloud-based service. SharePoint is widely used by large organizations for document storage and collaboration, often integrated with other Microsoft products such as Office and Outlook.
The attacks reportedly began on 7 July, with hackers attempting to breach systems through these weaknesses to gain initial access to targeted organizations. The flaws allow attackers to bypass authentication and remotely execute malicious code. In some cases, hackers sent requests to SharePoint servers to steal critical security keys.
Microsoft has since released security patches and urged all on-premises SharePoint users to install them. It warned with "high confidence" that the hacking groups would continue targeting systems that remain unpatched.
Linen Typhoon, active since 2012, has primarily focused on stealing intellectual property from government, defense, strategic planning, and human rights organizations. Violet Typhoon, operational since 2015, has engaged in espionage, targeting former government and military personnel, NGOs, think tanks, universities, media, and financial and health sectors in the U.S., Europe, and East Asia.
Microsoft stated with "medium confidence" that Storm-2603 is based in China but found no direct links to other Chinese hacking groups. It also cautioned that additional attackers may exploit similar vulnerabilities if security updates are not applied.
Read next
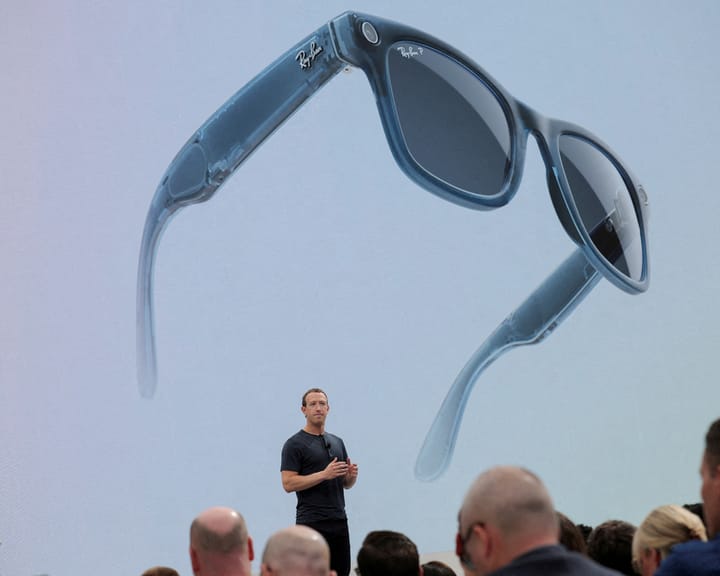
US officers worry Meta smart glasses could covertly record them
In January, the NYPD’s counterterrorism unit warned officers about a new security threat: Ray-Ban Meta glasses. A memo directed officers to “conduct thorough inspections of all eyewear permitted within inmate cells,” cautioning that recently arrested individuals could use the devices’ small cameras and microphones to record inside police
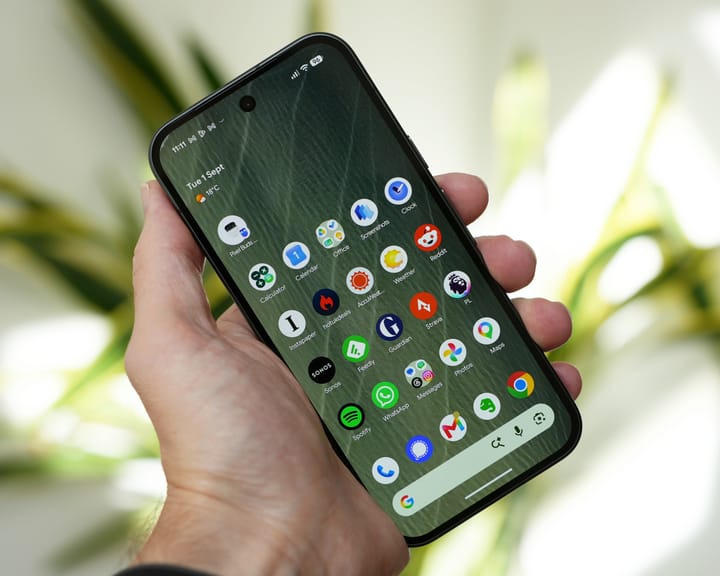
Google's Pixel 11 sets new standard for flagship phones, review finds
Google’s Pixel 11 continues to define what a base flagship phone should deliver, with leading cameras, extended software support and nearly all the features of its pricier siblings.
The standard Pixel 11 is priced at £879 (€999/$899/A$1,499), £80 higher than its previous version, reflecting ongoing
AI Expert Father of Three Shares Essential Insights for Parents on Artificial Intelligence
A father once promised his child they would write a story together called "The Day Nobody Went to Disneyland." The plot imagined a perfect day when the entire world avoided the park, expecting crowds, leaving it completely empty for a father and child to enjoy alone. Three decades